You must log in or register to comment.
 14 days
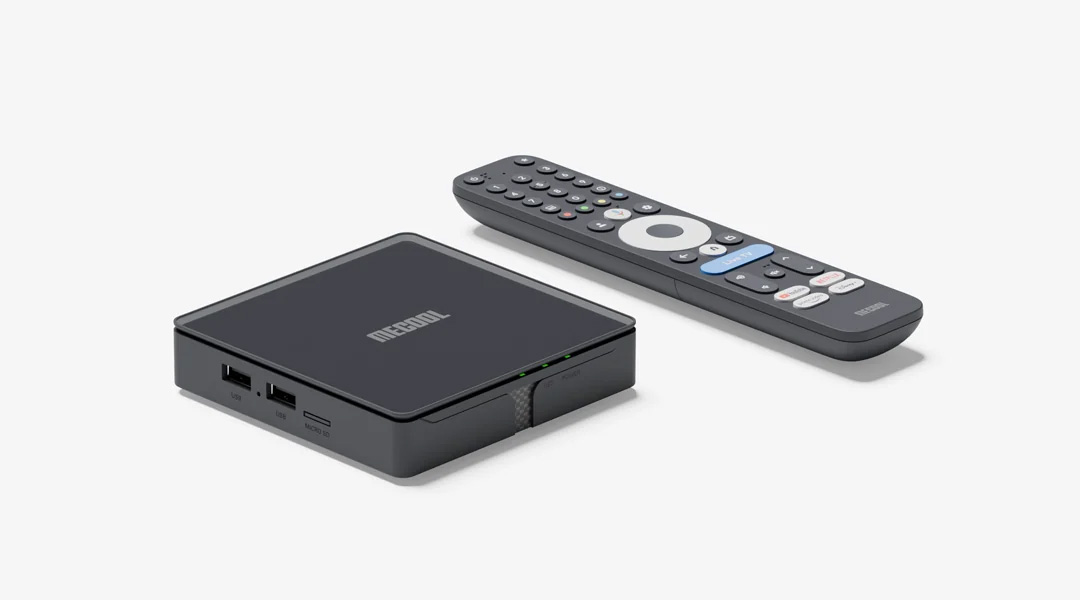
Google certified the boxes, the manufacturer installed a backdoor, and 1.3 million customers got an involuntary side hustle as residential proxies. Now the botnet is disconnected, but the malware remains and Play Protect is still disabled. Apparently »certified« just means the box passed inspection before it started spying.
- Quetzalcutlass@lemmy.worldEnglish14 days
“Looks good to me.” It’s a standard phrase used when signing off on changes.
Thanks. As an ESL, somehow I never come across that short form despite being online as a teenager since the 00s.
- 14 days
Tbh, English is my first language and I didn’t know that one either… And I’ve also been online since I was a teenager in the aughts.
- Quetzalcutlass@lemmy.worldEnglish14 days
It’s not a common term outside its niche. If you’re not in the industry, you’ll mostly see it used in pull request reviews by people who have professional backgrounds. Looks like it actually originated with Google.
It’s mostly used in code reviews, I wouldn’t say it’s general online slang.
- fragrantvegetable@sopuli.xyzEnglish14 days
I always thought it meant “Let’s get this merged”! 😆 Turns out I read this wrong for years.
- MonkderVierte@lemmy.zipEnglish14 days
Videostrong’s compromised boxes, mostly sold under the MECOOL brand
- kepix@lemmy.worldEnglish13 days
shame, they make good droid tv boxes. easy to smart up your ancient tv
- ozymandias117@lemmy.worldEnglish13 days
Google dismantles botnet
But then, no updates are applied to affected devices, and
Google worked with several other organizations to disrupt the x.cpe network, including Japan’s National Police Agency, Synthient, and Trend Micro. Google says it has taken legal action to shut down the domains and servers Videostrong
Sounds more like Google asked these other people to dismantle a botnet after detecting it.
The headline implies they somehow stopped it through Google Play
- Zeus@feddit.orgEnglish14 days
my android TV device isn’t google certified and I run a VPN with an adblocking DNS on it. I stream HD video with it whenever I have it on, what should I be looking for if I have a bad one?
- Peffse@lemmy.worldEnglish14 days
arstechnica linked to this location to identify if you have a model/package that is infected. It’s a looooong list.
I see where you are coming from, and I agree that amazon shits on privacy. But this is another level compared to “only” spying on your users. From the article:
After devices appeared online, a stub application called x.cpe or com.oemservice would phone home. This package did not have any malicious capabilities of its own, but it had the system-level permissions necessary to install malware modules at the operator’s behest. It also disabled Play Protect, which would have otherwise flagged the silently installed packages as malicious.
- neo2478@sh.itjust.worksEnglish14 days
Oh I completely agree. Also I don’t doubt those other boxes were also invading peoples privacy.
- fragrantvegetable@sopuli.xyzEnglish14 days
I’ve been looking for a box to replace my Chromecast for a while now but was hesitant for precisely this reason. At some point I even looked at the MECOOL boxes. Good my paranoia prevailed. Still looking for an TV box though. Any suggestions?
- Zarobi@aussie.zoneEnglish14 days
This might sound silly, but I ended up just hooking up my PC to the TV via HDMI. I just have a wireless mouse and keyboard and it can do all the things
- fragrantvegetable@sopuli.xyzEnglish14 days
If I was living by myself I’d probably go this route, but as it stands an android box with a remote is just easier for everyone else.
- Saltarello@lemmy.worldEnglish14 days
I would go mini PC with Jellyfin but a friend of mine bought a Formuler Z12 Ultra & flashed CoreElec with Kodi & seems pleased with it
Original article with full write up: https://cloud.google.com/blog/topics/threat-intelligence/shutting-the-door-on-the-xcpe-botnet/
- 14 days
Someone I know has one of these.
KD1:/ $ pm list packages | grep cpe
package:x.cpe
KD1:/ $ settings get global package_verifier_user_consent
1
Hmmmmmmmmmmmmmmmmmmmmmmmmmmmmmmmmmm, so Play Protect is enabled and doing nothing about it. Also, “nexus” wasn’t installed, not here at least. Not “system.ntp”, “oemservice” or “sso” either.
com.droidlogic.*is just generic AmLogic crap, if there’s a backdoor in there it’s probably a different company. The Google article mentionslibexploit.so, which doesn’t exist with a quickfind. Neither doeslibjaguar.so.libbase.sois just a generic file present everywhere, nothing interesting instringsfor it. My guess is that it’s geographically locked.So I am not sure what I am supposed to do with that. I just ran
pm disable-useron it, hopefully that’s enough.