
                        ⢀
                     ⢠⣿
                  ⢠⣿⣿
               ⢠⣿⣿⣿
             ⢠⣿⣿⣿⣿⡄
       ⣠⣤⣾⣿⣿⣿⣿⣿⣷⣤⣄⠀⠀⠀⠀⠀
           ⣼⡟⢻⣿⡟⢻⣿⣆⠀⠀⠀⠀
           ⣿⣇⣸⣿⣇⣸⣿⣿⣆⠀⠀⠀
           ⣿⣿⣿⡟⠻⣿⣿⣿⣿⣦⠀⠀
           ⠸⣿⣿⣧⣤⣿⣿⣿⣿⣿⣷⣄
⠀            ⢿⣿⣿⣿⣿⣿⣿⣿⡿⢿⡿
⠀            ⠈⢿⣿⡿⠋⠙⠿⠿⠁


new_otters_raft
Please contact me at @otter@lemmy.ca for any urgent issues.
This is an alt account used for testing and scheduling posts. I have retired the previous accounts I used for this purpose ( otters_raft@lemmy.ca and otters_raft@piefed.ca )
profile image: Photo by Kedar Gadge
- 8 posts
- 0 comments
Joined 8 months ago
Cake day: February 15th, 2026
You are not logged in. If you use a Fediverse account that is able to follow users, you can follow this user.
The excerpts below are from the following sources
https://www.theguardian.com/us-news/2026/sep/29/cornell-texts-rape-investigation
https://www.theglobeandmail.com/world/article-cornell-university-gang-rape-lawsuit/
The woman, identified only by a pseudonym in the lawsuit, filed the complaint Sept. 16, saying she was sexually assaulted at the Chi Phi fraternity house on the Ivy League campus in October 2024 after being pressured into snorting ketamine, smoking marijuana and drinking alcohol. She became completely incapacitated while frat members were sexually assaulting her, the lawsuit alleges.
Two of the alleged perpetrators were subsequently expelled after an internal investigation by Cornell – while the other five were allowed to resume their studies at the Ivy League institution after writing an essay, attending a workshop, or serving a short suspension.
None were ever arrested or charged, and outrage over the treatment of the alleged offenders grew when the woman’s lawsuit was made public.
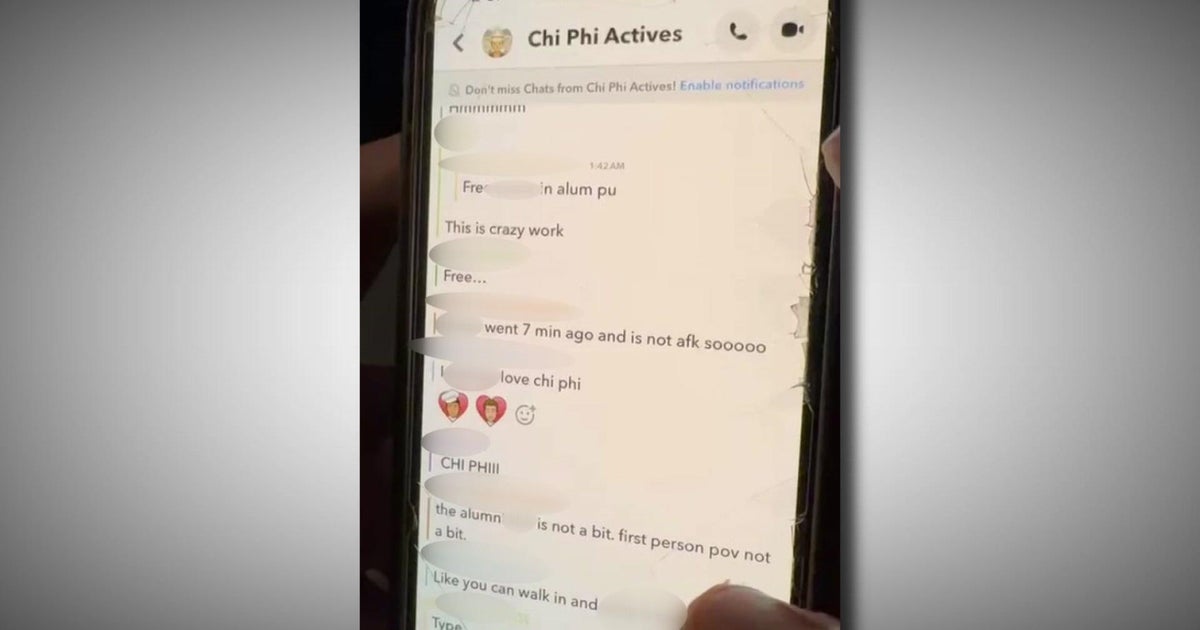
CBS, meanwhile, also claimed to have a video of Snapchat messages exchanged on the night of the alleged assault by numerous members of a group called Chi Phi Actives. One of the messages, sent while the woman was in the since-closed fraternity house, allegedly stated there was “free pussy upstairs”.
According to CBS, a later message sent by a group member asked: “Shop still open?” The response was, “Yea”.
Attorney Thomas Giuffra, who represents the woman, confirmed to CBS that his client – named Jane Doe in court documents – exchanged text messages with one defendant after the alleged assault. But Giuffra said he could not be certain the screenshots that CBS News saw were authentic.
The woman’s lawyer says Cornell University Police had the fraternity messages in 2024, but prosecutors say they didn’t see them until she filed a lawsuit recently
Over the weekend, New York Democratic Rep. Alexandria Ocasio-Cortez condemned what she called a “culture of rape” that is protected at elite institutions.
“When I read what happened at Cornell, those men posted in a group chat. That means it was normal to them. That means it was acceptable to them. This is a culture,” she said Sunday at a forum packed with young people near Cornell’s campus.
“And what we must do is understand that we cannot protect those spaces any more.”

c:geo is an open source geocaching app on Android. See the linked release for the full changelog

CWA is an eBook manager, and it is popular in the selfhosted book space. Please see the changelog link for the full summary, it is well organized and so I didn’t copy it here.

The latest versions of Common Voice datasets, Scripted Speech v27.0 and Spontaneous Speech v5.0, are available for download on the Mozilla Data Collective! A giant thank you to all of our contributors for their hard work putting together these datasets.
What’s new in this release:
Version 27.0 of Scripted Speech includes datasets for 295 languages. These datasets contain 32,349,999 voice clips, making approximately 42,593 hours of speech data available for developing and improving speech technology.
Version 5.0 of Spontaneous Speech includes datasets in 80 languages. These datasets contain 89,754 voice clips of free-form answers to questions, of which 302 hours have been transcribed and validated.Since the last release, the Common Voice community has welcomed 1 language to Scripted Speech - Pa’O (blk) - and 6 languages to Spontaneous Speech - Chinese (China, zh-CN), Swahili (sw), Palauan (pau), Sundanese (su), Bengali (bn) and Shan (shn).

TIL that Tailwind CSS is Canadian lol
Ottawa-based Shopify is acquiring Tailwind Labs, the Canadian company behind the popular, free, open-source web development framework Tailwind CSS.


Remember the original Quest headset that Meta (then Oculus) trumpeted back in 2019? Meta seems to hope you don’t, since the company officially stopped supporting the wireless VR headset in 2023 to focus on the more popular Quests 2 and 3. However, tinkerers haven’t abandoned the hardware and recently released a new root-access exploit and bootloader that gives “developers and enthusiasts full control over Quest 1 hardware.”
The QuestStack project integrates previously known vulnerabilities in the Quest’s Android fastboot process into a privilege escalation chain that leads easily to full root access on the device. The bootloading process is now streamlined enough that it can be completed without any downloads through a web interface after connecting the headset to a PC.
With this exploit, the original Quest hardware can now be officially divorced from any reliance on Meta’s servers or services to be useful. That means enterprising Quest owners should be able to sideload apps without needing to register for a Meta Developer account and activating Developer Mode through Meta’s mobile app. It also means users should be able to go through the initial setup and login steps for a fresh Quest headset even if and when Meta decides to shut down the servers that currently support this process.
This feels like bad design
Smart pet-feeder company Petlibro suffered an outage on Tuesday, giving users a harsh reminder of the risks of relying on smart devices.
Petlibro makes pet feeders that connect to Wi-Fi and, for setup with Petlibro’s mobile companion app, Bluetooth. Users can set the feeders to automatically dispense food at scheduled times, which is handy for pet care when the owner is out of the home.
In a statement to The Verge, Petlibro CEO York Wu said this week’s outage was “related to how the Petlibro app communicates with devices through its online servers.”
Some user reports have also conflicted with Petlibro’s claims about offline functionality. As The Verge pointed out, various users online claimed that during the outage, their devices did not perform any scheduled feedings, performed some feedings but not others, or performed feedings late (examples here, here, here, here, and here).