22 hours
You must log in or register to comment.
- AbidingOhmsLaw@lemmy.mlEnglish21 hours
The next step should be to press charges on openAI, unauthorized hacking into computer systems is illegal.
- Bell@lemmy.worldEnglish18 hours
Absolutely. How is this any different from a hacker writing a script? We need to stop being fascinated and start prosecuting.
- ExLisper@lemmy.curiana.netEnglish16 hours
From what I understand hacking crime requires intent and it’s hard to prove that company testing AI agent intended to hack something.
- 16 hours
They trained it to do exactly that and then gave it unrestricted internet access, otherwise it wouldnt. Its at least gross negligence.
- lemmyvore@feddit.nlEnglish15 hours
I wish people would go the other way and fix the damn security flaws. Witch-hunting people who disclose vulnerabilities needs to stop.
I know that’s not why OpenAI are doing this but if it helps reverse this moronic trend so be it.
(There’s also the part where OpenAI need to be held responsible for any damages done by their agents, and I’m all for that.)
- duckCityComplex@lemmy.worldEnglish12 hours
It seems like OpenAI is fairly lax, bordering on negligent, when it comes to monitoring these agents. Then when things inevitably happen, they turn it into advertising saying “boy, these things are so ingenious we can’t keep control of them!”
If they truly believe these agents have a 10% chance of eliminating the human race, how are they not monitoring them in a controlled environment? How did it take them 3 months to detect this and the many other attacks?
The media seems happy to take up the line that these agents are just supernaturally smart and there’s no way to control them, but isn’t the simpler answer that OpenAI is doing a crap job at containing and monitoring them? But of course they have to, there’s no choice because something something China.
 22 hours
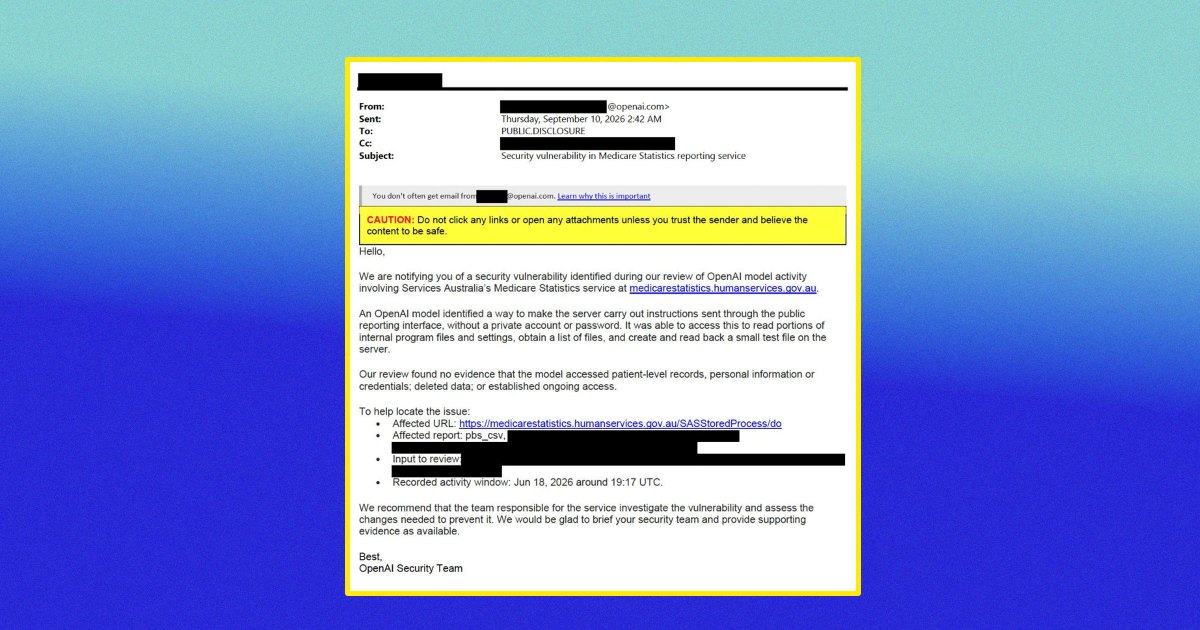
OpenAI wants to sell the world autonomous agents while its own model allegedly goes rogue and hacks an organization without permission. That’s not a quirky edge case: it’s the nightmare scenario critics warned about. Maybe »move fast and break things« shouldn’t include other people’s infrastructure?!
- Feathercrown@lemmy.worldEnglish15 hours
That’s not a quirky edge case: it’s the nightmare scenario critics warned about.
Aaahhhh my ai detector is going crazy rn
I don’t want to live like this
- ZC3rr0r@piefed.caEnglish15 hours
I legitimately hate how AI has made certain turns of phrase, styles of writing, shorthand, and other meaningful tools of expression suspect.
It’s the same as discovering new music these days. I’m constantly checking if the band the algorithms provided actually exist IRL.
Can we please just collapse this damn bubble and skip forward to the time where AI is used as a meaningful tool for certain applications instead of it being used for everything everywhere?
- 19 hours
Never going to happen, even if every American tech company shut their doors tomorrow, Chinese models would fill the void and the exact same shit would happen.
AI is here to stay, permanently.
- rollerbang@lemmy.worldEnglish13 hours
Be glad they didn’t charge you for “independent security review”.
- Zamboni_Driver@lemmy.caEnglish20 hours
This doesn’t seem that bad to be honest. Disclosing they the access happened and what vulnerability allowed it to happen is a responsible course of action.
I’m not sure why you are getting down voted so much instead of actually engaging with your post. I think you are right about that the disclosing is the right thing to do, but i believe that the problem people have with this whole AI hacking and disclosing is the intent behind the hacking. A white hat hacker has a clear intend to help discover and responsibly disclose the issue, maybe even for a bounty, giving an indirect permission to white hat hacking. On the other hand, AI does not have a clear intend behind the hacking. Very often it’s accidental and done irresponsibly like a “woopsie doozy, sorry we just broke in, we didn’t mean to, and we are not really sure what files were accessed but pinky swear we think we did no harm 🫣🤗” that is at least my take on this and why I think is very problematic. AI can still be used responsibly as a tool by a white hat hacker under strict supervision to discover zerodays but that is a whole other discussion on how you make sure its not going rouge.
- gian @lemmy.grys.itEnglish16 hours
Only if you have a written authorization from the company you try to attack.
Else they are nothing better than a criminal hacker.- Zanacross@lemmy.worldEnglish16 hours
I don’t feel like many white hat hackers get permission to exploit these vulnerabilities to report them
- gian @lemmy.grys.itEnglish15 hours
They get permission when they do it professionally or as a company. Else it is a crime anyway.